 The Assurance Desk
All 16 policy sets explained data limits, but only eight gave an explicit route for reporting a mistake or concern. The Assurance Desk read public policies and staff guidance from UK councils, education bodies and charities on 19 October 2026. The useful test for your policy is simple: can a colleague find what to do next?
What does a usable workplace AI policy answer?
Picture a colleague about to use AI to draft a customer email. They need to know which account to use, what they can paste in, what to check and who can help. A broad call to use AI responsibly leaves those practical questions open. Use that work task as the starting point for your policy review.
A public Hacker News question puts the problem in plain words. It asks whether employers have a real policy or rely on common sense. It is a question, not a verified account of an employer’s practice. These quotations were checked against saved readings of public posts, which may not show later edits.
We tested eight everyday questions against each of the 16 policy sets. An explicit answer had to meet a rule set before coding began, such as naming a reporting contact or a usable route. A general reference to another internal procedure was only partial.
Data limits were the most consistent answer. All 16 sets gave a practical boundary on information use. Fifteen said what to check in AI output. Approval and reporting were less often explicit, at nine and eight respectively. These counts describe the public text we reviewed, not all UK workplaces.
| Staff question | Explicit | Partial | Not found in public text | Unavailable text |
|---|---|---|---|---|
| Tool and account | 10 | 5 | 1 | 0 |
| Data limits | 16 | 0 | 0 | 0 |
| Checks on the answer | 15 | 1 | 0 | 0 |
| When to disclose AI use | 13 | 2 | 0 | 1 |
| Approval for a new use | 9 | 7 | 0 | 0 |
| Reporting a mistake | 8 | 4 | 3 | 1 |
| Training or help | 13 | 3 | 0 | 0 |
| Actions AI may take | 12 | 1 | 2 | 1 |
does your company have real AI usage policy or is it "use common sense"?
Where should someone report an AI mistake?
Give staff a named contact or a route they can follow. In our review, eight policy sets made that explicit. Four referred more broadly to reporting or other procedures. Three had no route we could find in the public text, and one had relevant text we could not read. Those last groups do not prove that an internal route is missing.
The UK Department for Work and Pensions provides a concrete example outside our counted sample. Its policy tells users to report AI misuse to their line manager and, where required, the Security Incident Response Team. That gives a colleague a place to start.
Links can carry part of the answer. Six of our 16 main documents gave an explicit reporting route. Reading directly linked material brought that to eight. This is a different view of the same policies, not an improvement measured over time.
Try this with a colleague: ask them to find the reporting route without help. If they reach a page they cannot open, record that as a problem to fix. A policy review should test the journey as well as the words.
| Reading scope | Explicit routes | Policy sets reviewed |
|---|---|---|
| Main document only | 6 | 16 |
| Including directly linked material | 8 | 16 |
A named starting point: DWP’s published reporting instruction. This example is outside the counted sample.
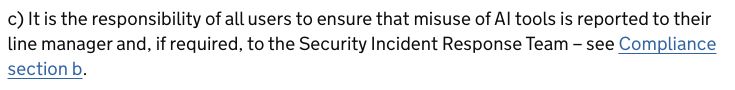
The instruction names the line manager first, then the Security Incident Response Team if required. The crop shows the original wording without colour changes.
Department for Work and Pensions, Crown copyright, Open Government Licence. Captured 19 October 2026. View full size · Image licence
Approve the task, not just the tool
Ask what the tool will do in this particular task. Drafting a message for someone to check is a different request from giving AI access to work systems. Your review should spell out the intended use, the person who can approve it and the limits on access.
The DWP policy requires fresh approval when an approved tool’s use changes significantly. It gives using personal data for the first time as an example. Approval comes from the relevant governance board, the group responsible for that decision.
Our sample offers practical routes too. Spelthorne Borough Council tells staff exploring a different use to contact its Projects Team. Lymphoma Action requires approval before an AI agent is used. A senior management member of its AI Working Group must agree, along with at least one other group member.
For access to other systems, York Diocesan Board of Finance tells staff to allow only the minimum permissions needed. That is a useful question to add beside the tool name: what will it be allowed to reach or change? This policy covers the board’s own staff, agency staff and volunteers, not parochial church council employees.
Name the access limit as well as the tool. An excerpt from York Diocesan Board of Finance’s published policy.
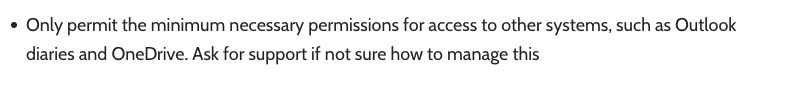
The policy says to allow only the minimum necessary permissions for access to other systems and to ask for support if unsure. The source screenshot is cropped, with no filter or annotation.
Diocese of York / York Diocesan Board of Finance. The policy page permits copying and adaptation. Captured 19 October 2026. View full size · Image licence
Test your policy with one real work task
Start with a task your team already wants to do. Ask a colleague to use the policy to answer the worksheet questions. For each answer, write down the rule, the contact or the link they would actually use. Leave an unanswered question visible rather than filling it with a guess.
Then make the checks concrete. The DWP policy, for example, asks users to check accuracy, reliability and credibility, including misinformation and bias. For an email draft, you could turn that into a review of names, claims and promises before anyone sends it. That email example is an exercise, not a finding about a studied employer.
Oliver Patel’s point about AI literacy fits this task. Knowing how to ask AI for an answer is only part of knowing how to use it at work. His quoted words are an expert opinion, separate from our policy counts.
Use the worksheet to agree what happens next. The task can proceed within the recorded limits, it needs approval, or it should not go ahead. Name an owner for each open question. The worksheet helps organise that discussion; completing it does not certify compliance.
Turn a policy into a decision
- Choose a task Write what you want AI to do and what information it would use.
- Find the answers Record the rule, contact or link for each staff question.
- Agree the next step Record the decision, limits and owner of anything still open.
AI literacy means much more than knowing how to prompt
How did we check the policies?
On 19 October 2026, we screened a fixed list of 20 UK organisations. Sixteen had enough issued public policy or staff guidance to include: five councils, seven education bodies and four charities. Two sources were unavailable. For two others, we could not confirm the final amended policy text. We excluded those four rather than treating them as policies with missing answers.
One editor read the documents and directly linked material, coded them against the eight questions, then rechecked the evidence. The dataset records each decision and the original links. This was not an independent second review. We also screened 85 stored public-discussion records to help shape the questions. Those records are not 85 people or companies, and we did not use them to estimate how common a problem is.
An explicit answer met the question’s preset rule. Partial meant that relevant wording did not fully meet it. Not found means we did not find an answer in the public text. Unavailable means relevant text could not be read. None of those labels assesses an employer’s legal compliance.
Scope matters. Some education policies cover only research, teaching or administration. Exeter’s full policy requires a login, so we used its public staff guidance and kept unreadable answers separate. This is a study of published wording, not a survey of what employees know or do. It does not represent all UK employers or private businesses.
We checked how much the education documents affected the result. With them removed, all nine remaining sets still gave data limits and six gave an explicit reporting route. The gap remained, but the counts changed. Both this check and the main-document-only counts are in the download. Policies may change after the reading date.
Explore the data
Download the dataset or open the cited links in a spreadsheet.
Read next
Sources
- The Assurance Desk, workplace AI policy study, checked 19 October 2026
- partycat, Hacker News question, checked 19 October 2026
- GOV.UK, Artificial Intelligence Security Policy, checked 19 October 2026
- Diocese of York / York Diocesan Board of Finance public policy, checked 19 October 2026
- Oliver Patel on LinkedIn, 5 Foundational Skills for AI Literacy Beyond Prompt Engineering, Oliver Patel, AIGP, CIPP/E, MSc posted on the topic, checked 19 October 2026
- Lymphoma Action public policy, checked 19 October 2026
- Spelthorne Borough Council public policy, checked 19 October 2026
This is an independent editorial guide, not legal advice.