 The Assurance Desk
What is ISO 27001?
ISO/IEC 27001 is the international standard for an information security management system. It describes how an organisation runs information security as an ongoing system, rather than listing technical controls to install once. ISO and the IEC publish it jointly, and the current edition is the third, published in October 2022.
Its full title is Information security, cybersecurity and privacy protection, Information security management systems, Requirements.
Readers with a United Kingdom billing address buy the standard from the BSI store.
What does certification involve?
ISO 27001 certification has two halves. First you build and run the information security management system the standard requires. Then an independent certification body audits it and decides whether it meets the requirements. ISO/IEC 17021-1 sets the rules for those bodies, covering their competence, consistency and impartiality.
ISO/IEC 17021-1 also says a certification body does not need to offer every type of management system certification. That matters most when you choose one.
From a security system to a certificate
- Build and run Put the information security management system into practice.
- Check the body Read its accredited scope for the standard you need.
- Independent audit The certification body audits the system and decides whether it meets the requirements.
How do you check a certification body?
To check a certification body in the UK, read its schedule of accreditation in the UKAS directory of accredited organisations. The schedule lists the standards the body is accredited to certify. Read it for the standard you want, because accreditation for one does not carry across to another.
UKAS is the national accreditation body for the United Kingdom, appointed by government to assess organisations that provide certification, testing, inspection and calibration services.
You can search the directory by organisation type, including certification bodies.
The clearest current example is the AI management system standard, ISO/IEC 42001. Some bodies accredited for ISO 27001 are also accredited for ISO 42001. Others are not yet, and their schedules say so.
On this site, 33 of the 140 providers are certification bodies, and each profile records what its UKAS schedule showed on the date we read it.
Where to check a certification body
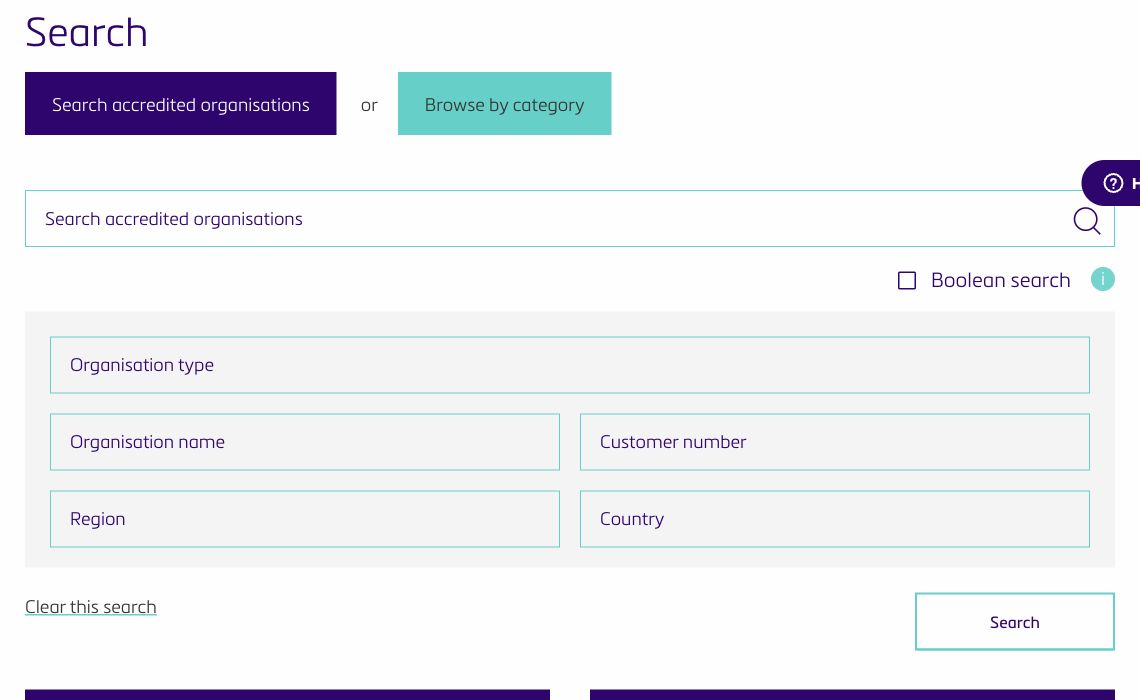
The screen shows a search box and filters for organisation type, organisation name, customer number, region and country. It also offers a Boolean search option, a Search button and Clear this search. Choose Certification Bodies as the organisation type when checking who can certify you. The search screen itself is not proof of accreditation. Read the organisation’s schedule for the relevant standard.
UKAS website, © UKAS. Cropped screenshot for the directory walkthrough. Captured 7 October 2026. View full size
Is Cyber Essentials the same thing?
No, Cyber Essentials is not the same thing as ISO 27001. It is a separate United Kingdom scheme, the minimum standard of cyber security recommended by the government, developed by the National Cyber Security Centre (NCSC) and built around five technical controls: firewalls, secure configuration, security update management, user access control, and malware protection.
IASME is the NCSC's official Cyber Essentials delivery partner and manages a network of more than 400 cyber security organisations across the United Kingdom.
Certification is renewed annually. There are two routes: a self led route where you complete a verified self assessment, and a supported route where you pay for help from a Cyber Advisor or a certification body.
IASME publishes the price by organisation size: £320 plus VAT for nought to nine employees, £440 for ten to 49, £500 for 50 to 249, and £600 for 250 or more.
Cyber Essentials Plus is a technical audit of your systems. The verified self assessment is a prerequisite for it, and you contact a certification body directly to arrange it.
| Route | What it covers | What to check |
|---|---|---|
| ISO/IEC 27001 | An information security management system | The certification body’s accreditation for this standard |
| Cyber Essentials | Five technical cyber security controls | The verified self assessment and annual renewal |
| Cyber Essentials Plus | A technical audit of your systems | The Cyber Essentials self assessment is a prerequisite |
What to do
- Decide which standard the person asking actually wants. A customer asking for 'security certification' may mean ISO 27001, Cyber Essentials, or something else.
- If it is ISO 27001, look up any certification body in the UKAS directory of accredited organisations and read its schedule of accreditation for that standard before you engage it.
- If a body is not listed for the standard you want, ask it directly what its accreditation covers. There are reasons a body may not be accredited for a given standard yet.
- If it is Cyber Essentials, start with the free resources and the price bands published by IASME, and decide between the self led and supported routes.
- If you need Cyber Essentials Plus, remember the self assessment comes first, then the technical audit.
Common questions
Can the firm that helps me prepare also certify me?
No, not for an accredited ISO certificate such as ISO 27001. The certification body may not also offer consultancy on management systems, so your own team or a different firm does the preparation. The rule comes from ISO/IEC 17021-1, the standard that sets the impartiality rules for certification bodies. If one group offers both, ask which company issues the certificate and under which accreditation. See can the firm that prepares you also certify you?
Does ISO 27001 certification cover AI?
ISO 27001 covers information security management. AI management systems are a separate standard, ISO/IEC 42001, and accreditation for it is separate too. A body accredited for one is not automatically accredited for the other. See our guide to ISO/IEC 42001 certification.
Is Cyber Essentials enough on its own?
It depends on what you are being asked for. Cyber Essentials is described by the NCSC as the minimum standard of cyber security recommended by the government. Some contracts ask for it specifically. Others ask for ISO 27001, which is a management system standard and a larger undertaking.
How do I read a schedule of accreditation?
Find the body in the UKAS directory of accredited organisations, open its schedule, and look for the standard you want. The schedule lists what the body is accredited to certify. It is the document UKAS itself publishes, so it settles the question.
Where next
Sources
- ISO/IEC 27001:2022, Information security management systems, ISO, checked 30 September 2026
- ISO/IEC 17021-1:2015, Requirements for bodies providing audit and certification of management systems, ISO, checked 30 September 2026
- UKAS directory of accredited organisations, checked 30 September 2026
- Cyber Essentials, National Cyber Security Centre, checked 30 September 2026
- Cyber Essentials, IASME, the NCSC's official delivery partner, checked 30 September 2026
- About UKAS, the national accreditation body for the United Kingdom, checked 30 September 2026
- European Accreditation, FAQ 41.1: impartiality, ISO/IEC 17021-1:2015 clause 5.2.5, checked 2 October 2026
This is an independent editorial guide, not legal advice.